AuditLink
AuditLink is a tool that facilitates the secure collection, packaging, and sharing of audit-related files. It enables users to gather documents and content linked to SAP objects (ArchiveLink only), organize them into audit bundles, and distribute those bundles to auditors or relevant personnel.
At the end of the process, AuditLink generates an optional HTML file that contains a summarized list of the all the collected contents.
There are 4 methods to run AuditLink:
- Delivered reports
- Customized or new reports by yourself the customer
- Best practice is to copy delivered report and change to suite your needs
- Excel Spreadsheet
- Direct ArchiveLink Table Selectdion
Refer to the section 'Execution' for User instructions on how to run the various methods.
Pre-Configuration Requirements
Setup Content Repositories, CMS profiles and tags, and RFC destination as part of a standard Link Enterprise implementation. These will enable RFC communication between SAP and external repository(ies).
SAP Security Requirements
Running AuditLink requires 2 types of SAP authorizations:
Link Enterprise SAP T-Code Authorization
- Mandatory: Any AuditLink End-User will need access to the below transaction to create AuditLink Bundles. This should be granted by your SAP Securitiy Team:
- /DFLOW/AUDITLINK
- Optional: For a user to view previously create AuditLink bundles (for everyone), the below transaction can be granted:
- /DFLOW/AUDITLINKDASH
Link Enterprise Global or Attachment Level Authorization
When you create a bundle, Link Enterprise checks its own config via transaction /dflow/sys and choose the menu path Configure->AuditLink->Security.
At least 1 entry in this table must exist. For details on this configuration, please refer to the section below labeled AuditLink Configuration #3: Security.
Bundle Location Configuration
The destination for saving audit bundles must be a mounted drive (e.g., network share or mapped drive) accessbile by both the SAP system (in the background) and the User. This is setup in the 3 elements of setup/configuration below. Albeit configured in different methods and syntax, these three elements must resolve to the exactly the same location (ie: be a 3-way match).
1) Transaction FILE
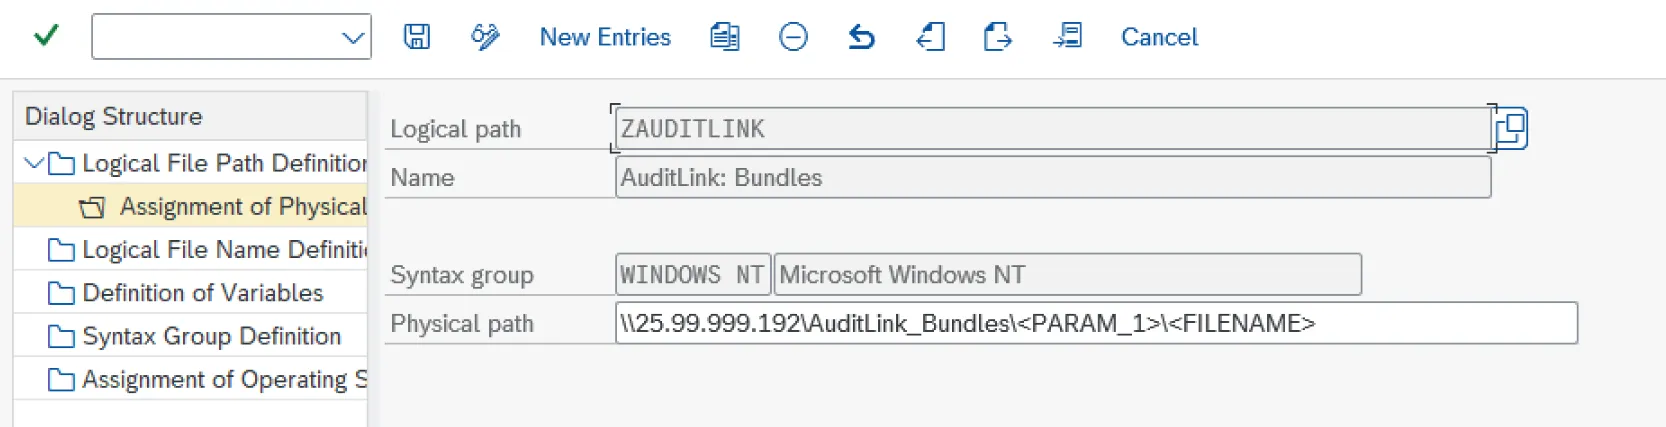
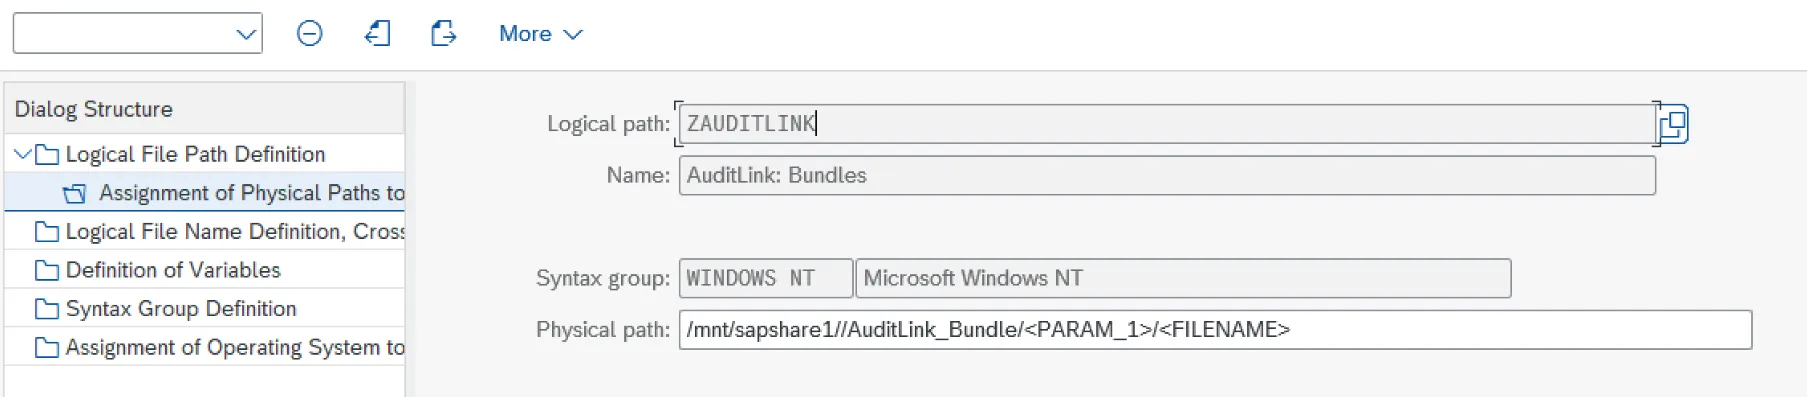
- Assign the physical path of the mounted drive to the logical path ZAUDITLINK using transaction FILE in SAP.
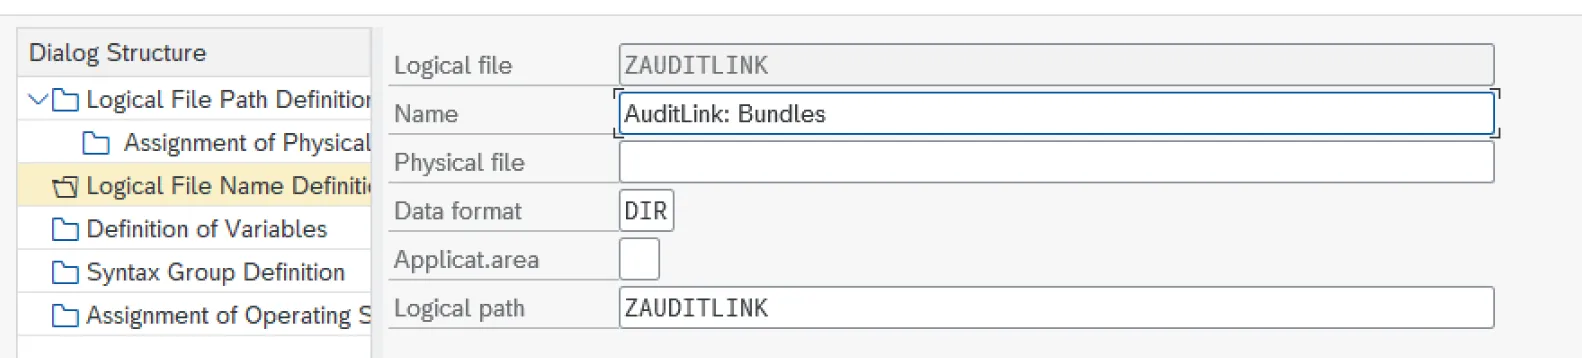
- You must create the ZAUDITLINK logical file and ZAUDITLINK file path in your system
- The destination (ie: home base for the bundles), albeit may not match in terms of format (example: Linux SAP system vs. windows network drive), must resolve to the same location as the User Workstation Accessbile drive below, as well as the section AuditLink Configurations 2.1.1 below.
- Confirm the mounted drive is properly connected to the SAP system, allowing read/write access during audit bundle generation.
- The physical path must have the parmaers <PARAM_1>\<FILENAME> in exact casing wih the '\' in between.
- Example of Logical File:
- Example of a Windows mounted drive logical path:
- Example of an Azure file share mount logical file path:
2) User Workstation (OS) Accessible
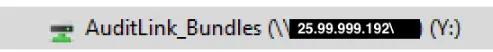
- Ensure the end user has appropriate read and write permissions to a mounted drive to the same location as the above FILE transaction as well as the section AuditLink Configurations 2.1.1 below.
- Example of user workstation windows share:
3) Bundle Locations
See section AuditLink Configurations 2.1.1 below.
Additional AuditLink Configuration
Configure the AuditLink rule via transaction /dflow/sys and choose the menu path Configure->AuditLink. There are four AuditLink rule elements to configure:
- Base Connectivity: Assign CMS tag to content repository. This tag identifies the RFC connection used to retrieve content from defined repository.
- Bundle Locations: Define allowed locations where users can save audit bundles. 1 "root" location configuration entry is required, user based locations are optional.
- WRoot Location: This must match the mounted drive in the "Transaction FILE" and "User Workstation Accessbile" location in the requirements outlined above.
- This entry is specified with a '*' in the user field. Example:
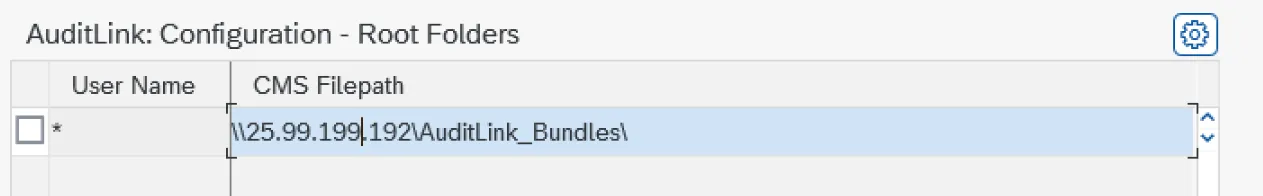
- User Location (optional): This entry is at the user ID level and forces a bundle to be created in a folder within the root location. This could be by user or by controlling area or however you wish to organize your bundles. This typically is only used when you want to keep certain bundles separate for security or organization reasons.
- Specify a location with no '\', just a folder name. Example:
-
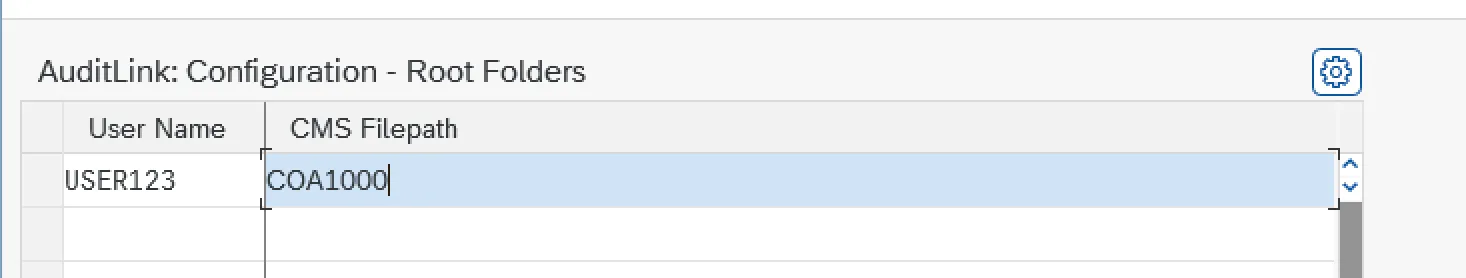
- NOTE: The folder COA1000 must ALREADY exist within the root location.
- Security: This table specifies whether or not to enforce an S_WFAR_OBJ authorization check. This can be used to prevent users who do not typcially have authorization to view attachments to still create bundles. This can be determined by:
- Option 1: A "global rule" level (* or user id) OR whether to enforace at attachment level using the .
- User ID Level: This is checked first. Leave all fields BLANK except for enter the SAP USER ID in the user name field. Example:
-
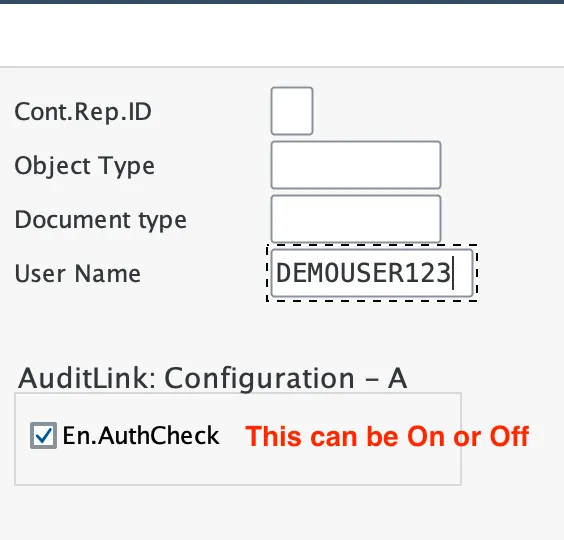
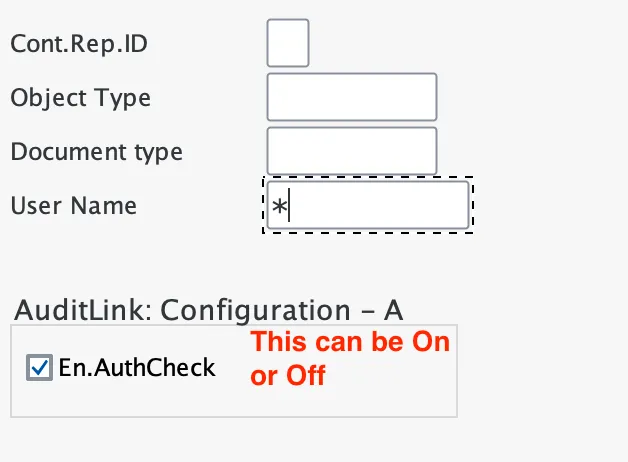
- Wildcard Level: This is checked 2nd. Leave all fields BLANK except for a * in the user name field. This is the most straight forward way to configuration AuditLink with or without S_WFAR_OBJ authorization (see below). Example:
- Option 2: This is only check if a global rule in Option 1 is not found. Based on content repository, SAP object, and document type. (note: user name field is ignored in this check). Do not uses *'s. This option will perform 4 levels of granularity:
- Exact match at Repository ID and SAP Object and DocType.
- Exact match at Repository ID and SAP Object. DocType left BLANK
- Exact match at Repository ID and DocType. SAP Object left BLANK
- Exact match at Repository ID. DocType and SAP Object left BLANK
- Regardless of which option, a rule must be found, and that rule determine whether S_WFAR_OBJ (Activity 03) is checked at the attachment level. This is determine by within the found rule, enabling/disabling the field "En.AuthCheck" as shown in the above example.
- Note: At least one entry is required in this table.
- Reports: Define reports to be executed when generating an audit bundle. Reports are based on a business object and tailored to the audit context.
- Incl. HeaderDocs: Include attachments at the header level of the document in the final bundle.
- Include HTML: Generate and include an HTML file summarizing the list of attachments. This file will be saved in the bundle folder.
- Include Results: Add a .TXT results file to the bundle, showing a summarized count of successfully retrieved attachments and noting any failures.
- Email: Send an automatic notification email to the user once the bundle creation process is complete.
- Run Auto: Automatically generates a bundle name using the current date, time, and SAP user. Skips manual naming prompts.